Find out if your app is safe before your customers do.
Apps built with AI tools, or handed over by an agency, often hide the same few problems: customer data anyone can read, payment keys in the browser, no backups. In five business days we check the parts that can hurt you and tell you, in plain language, what to fix first.
$1,500 fixed · credited toward any fix
Typical: 5 business days · written report + 45-minute walkthrough
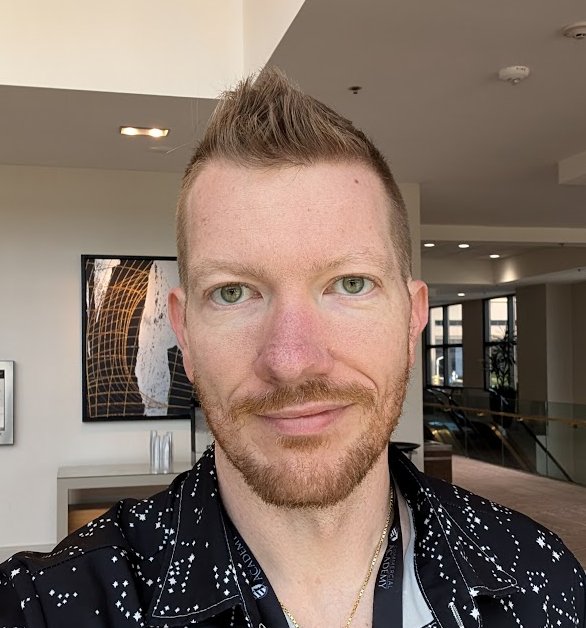
You'll talk to Nate, the engineer who does the work. No salespeople, no pitch, and an honest answer even if it isn't us.
This is for you if…
- 01
You're about to launch or start charging
Real customers, real payments and real data are coming. You want to know it's safe first.
- 02
AI wrote most of the code
It works in the demo, but nobody has checked what happens when someone pokes at it.
- 03
You inherited it
A freelancer, agency or former cofounder built it, and you can't judge it yourself.
- 04
You want a quick, honest read
Not a long engagement. A fixed price, a fixed date and a clear answer.
Proof, from the field.
- MSN-01Telehealth
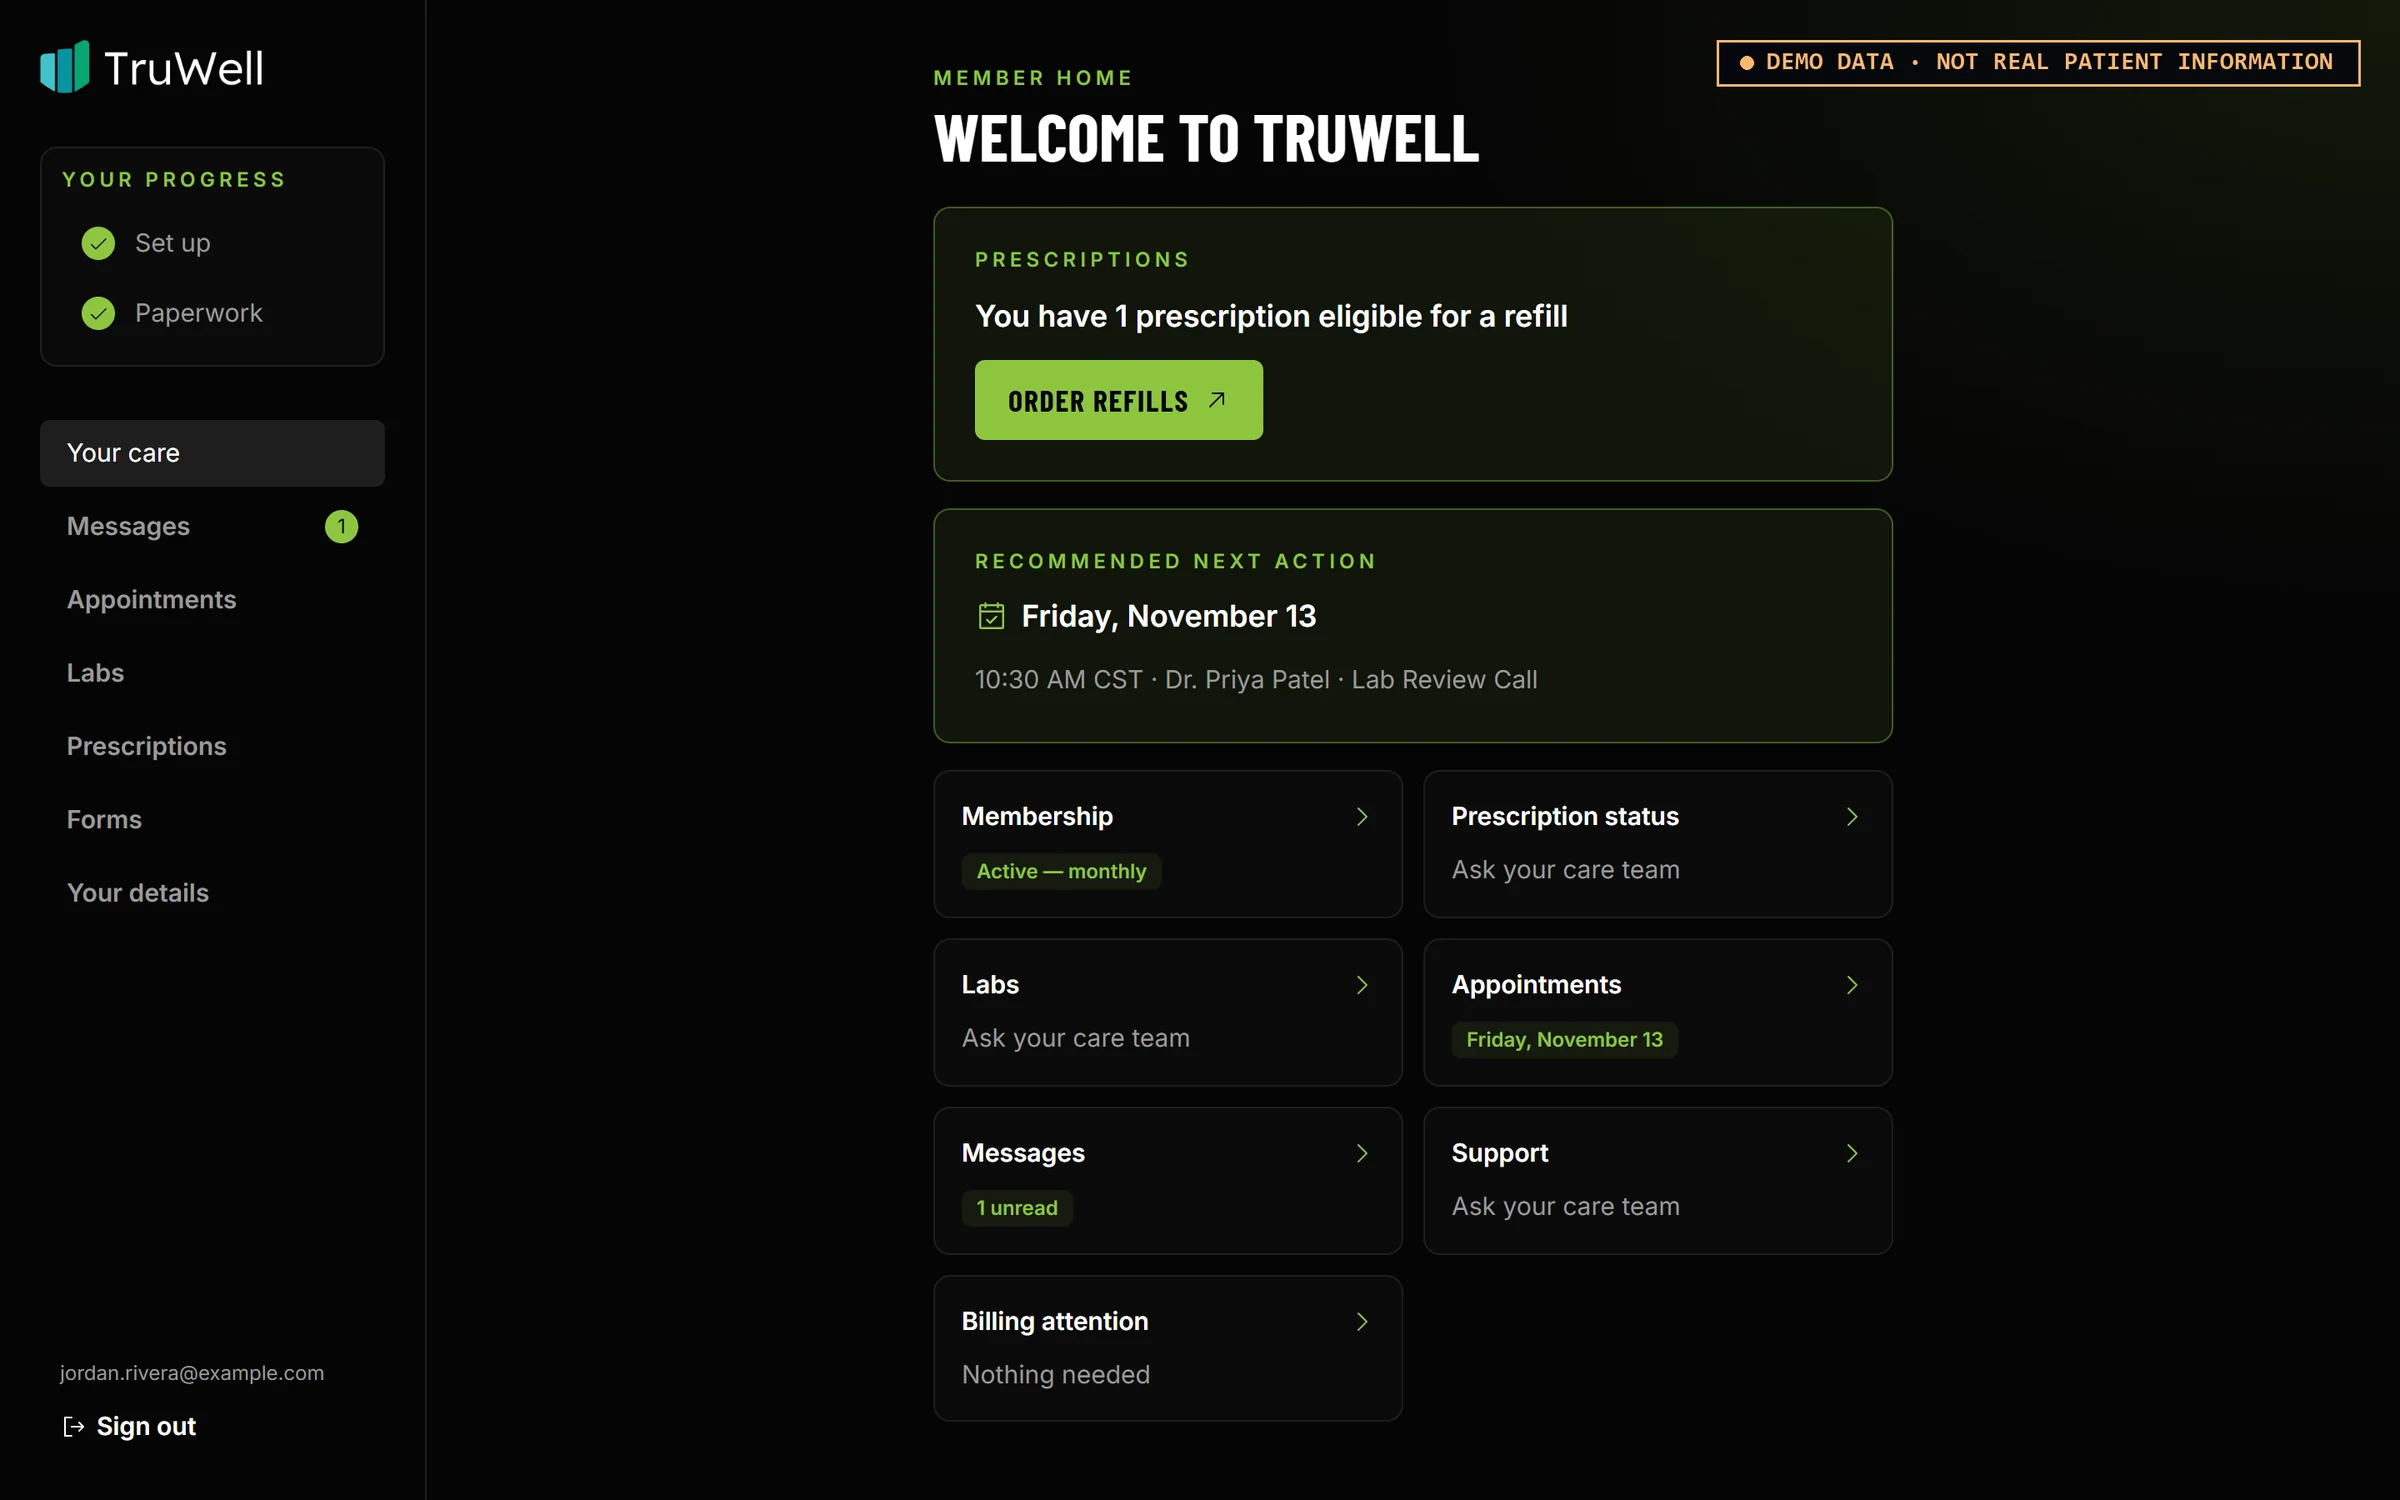
TruWell
1 monthFrom a half-working vibe-coded prototype to a production care app in one month, built around the patient experience the clinic wanted.
Read the case study - MSN-03PropTech / AI sales CRM
FlipIQ
50%Fractional CTO for a stalled platform rebuild: multi-tenant foundations, a real delivery process, half the hosting bill, and a product finally in customers' hands.
Read the case study
What you get.
- D-01
Logins and data access
Who can see and change what: database rules, row-level security, admin routes and user permissions.
- D-02
Secrets and payments
API keys, payment keys and webhooks checked for exposure in the browser, the repo and the hosting setup.
- D-03
Backups and recovery
Whether your data is backed up, and whether you could actually get it back.
- D-04
Hosting and deploys
Environments, who can reach production, and how risky a deploy is today.
- D-05
Ranked findings report
Every issue rated by risk and effort, in plain language, with the technical detail your developers need.
- D-06
45-minute walkthrough
We go through the report with you and answer every question. You leave knowing exactly what to do next.
How it runs.
- 01Day 1
Kickoff
A short call on what the app does and what's riding on it. You share read-only access.
- 02Days 2–4
Review
Automated scans plus a senior read of the code and settings that handle logins, money and data.
- 03Day 5
Report
A written report, ranked by risk, with a recommended fix and rough effort for each item.
- 04Within a week
Walkthrough
We walk you through it. Fix it yourself, hand it to your team, or have us do it with the $1,500 credited.
// Typical timings. We confirm yours in the written mission plan.
Questions we hear.
Something else on your mind? Ask it on the call. That's what it's for.
Book a free callHow is this different from the full code & security audit?
The Health Check is a fast, fixed-price look at the risks most likely to hurt you: data access, secrets, payments, backups and hosting. The full audit takes about two weeks and also covers architecture, code quality and due-diligence reporting.
What if you don't find anything serious?
Good news, and now you have it in writing, which is worth having when customers or investors ask.
How does the credit work?
If you hire us to fix what we find within 60 days, the full $1,500 comes off that project.
What access do you need?
Read-only access to the code repository, plus a view of the database and hosting settings. We never need to change anything to do the review.
Will you sign an NDA?
Yes. Send yours or we'll provide one, signed before you share anything.
// Tools we fly with
- Lovable
- Bolt
- Cursor
- Replit
- v0
- Supabase
- Firebase
- Node.js
- PostgreSQL
- Stripe
- Vercel
- Netlify
- AWS
- Cloudflare
Know what you're launching.
Book a quick call to start your Health Check. Fixed price, report in five business days.